What is Supply Chain Security? An explanation of implementation design and SCS evaluation systems to prevent procurement disruption risks.


"We've taken measures to prevent this, so why is procurement stopping?"
Much of the reason lies in "structural risks across the entire supply chain" that cannot be prevented by individual companies alone.
In fact, cases where intrusions via subcontractors or damage to supplier companies escalate, ultimately leading to production stoppages or Service disruptions, are already occurring in large corporations.
- Even if your company has robust security measures in place, intrusions can still occur through business partners.
- Due to damage to suppliers, deliveries have stopped, and business operations have been halted.
- Our company's customer information was leaked due to an accident at our outsourced company.
These risks are no longer just an IT department issue; they are Issue that directly impact procurement, sustainability, and management decision-making.
▼Do you have any of these Issue?
- We are unaware of the security status of our suppliers.
- Third-party risk management is becoming dependent on individual expertise.
- I don't know how to deal with the SCS evaluation system.
- The IT department is left to handle everything, and the procurement department is not involved.
- I'm struggling with how to incorporate security requirements into the contract.
→If even one of these applies to you, this document will help you organize your company's Issue and prioritize how to address them.
What you can learn from this document (based on the webinar Contents)
This document is based on the Contents of the webinar held on March 26, 2026 (title: Procurement Stops! Information security in the Supply Chain - Designing Implementations to Turn Risk into Competitiveness ), and has been restructured to focus solely on the webinar Contents. In this webinar, Kenichi Hirano, Vice President of MUFG GMO Security Company, Ltd., was invited as a guest speaker and spoke from the perspective of how to make Information security in the supply chain function across the entire supply chain, rather than focusing on individual measures.
- What is supply chain security? (Basic overview)
- Why are supply chains being targeted now?
- Actual damage patterns (business disruption, data breaches, intrusion into security systems)
- Key points and usage methods of the Ministry of Economy, Trade and Industry's "Security Measures Evaluation System for Strengthening Supply Chains (SCS Evaluation System)"
- Compliance with the European Cyber Resilience Act (CRA) and software embedded in Manufacturing lines and Manufacturing.
- The role of PSIRT (Product Security Incident Response Team)
- Practical points for collaboration between procurement and IT departments
- Designing effective communication with suppliers
- Impact on transaction decisions and contractual points
- Balancing data linkage, traceability, and security across the supply chain.
- Key points for engaging with management (balancing horror stories and best practices, rethinking security)
Table of contents for the full document that can be downloaded and read.
1. What is supply chain security? Why is it a Issue for procurement and sustainability departments?
2. The picture revealed by IPA's "Top 10 Threats"—Reading "Methods" and "Targets" separately
3. Four types of supply chain security risks and the key points covered in the webinar.
4. Common misconceptions: "B2B companies are not targeted," "Small and medium-sized enterprises don't have anything that would be a problem if stolen," "We've taken countermeasures once before, so we're protected."
5. Systemic Trends (Japan) – Defense, Automobiles, and the Ministry of Industry, Trade and Industry's SCS Evaluation System
6. Compatibility between European CRAs and software built into Manufacturing equipment, etc. — Answers to pre-submitted questions
7. Effective relationships with suppliers—co-creation rather than imposition
8. Immediate use and maturity level of the SCS evaluation system
9. Impact on contract and transaction decisions – Risk of transactions being halted without clear explanation of the decision's reasoning.
10. Data Integration, Traceability, and Security
11. How to involve senior management
12. Dataseed SAQ: A platform for streamlining survey distribution and response – Summary of features introduced in the webinar
13. For those in charge at large corporations: A readily usable "self-reflection checklist" (from the webinar Contents)
14. Glossary
15. Reference Links (Webinars, Related Press Releases)
If you would like to see more details, please register here.
We will send you the complete document via email.
To suppliers
Streamlined SAQ collection and management
Dataseed SAQ
For detailed information and Contact us about the entire Service ,
Please check here.
Related articles
-
Deciphering the Exposure Draft of the EU Disclosure Standard "ESRS-40a" for Non-EU Companies - Limitations on Impact and Value Chain Voluntary Standards (Public Comment Period Ends October 31)
-
Public comments on the revised GHG protocol Scope 2 have been released — Multiple methods to be considered due to disagreements over hourly matching, etc.
-
Measurement and Disclosure for Nature Positive "Implementation" - The Kumamoto Summit Showcased the Two Pillars of Impact and "Dependence"
-
What is Supply Chain Security? An explanation of implementation design and SCS evaluation systems to prevent procurement disruption risks.
Ongoing Webinars
-
[Recorded Broadcast] This is not someone else's problem—Why supply chains are becoming a management Issue: An interview with Kenji Fuma on how companies could have prepared and acted.
Location: Online (Zoom)Participation fee: Free -
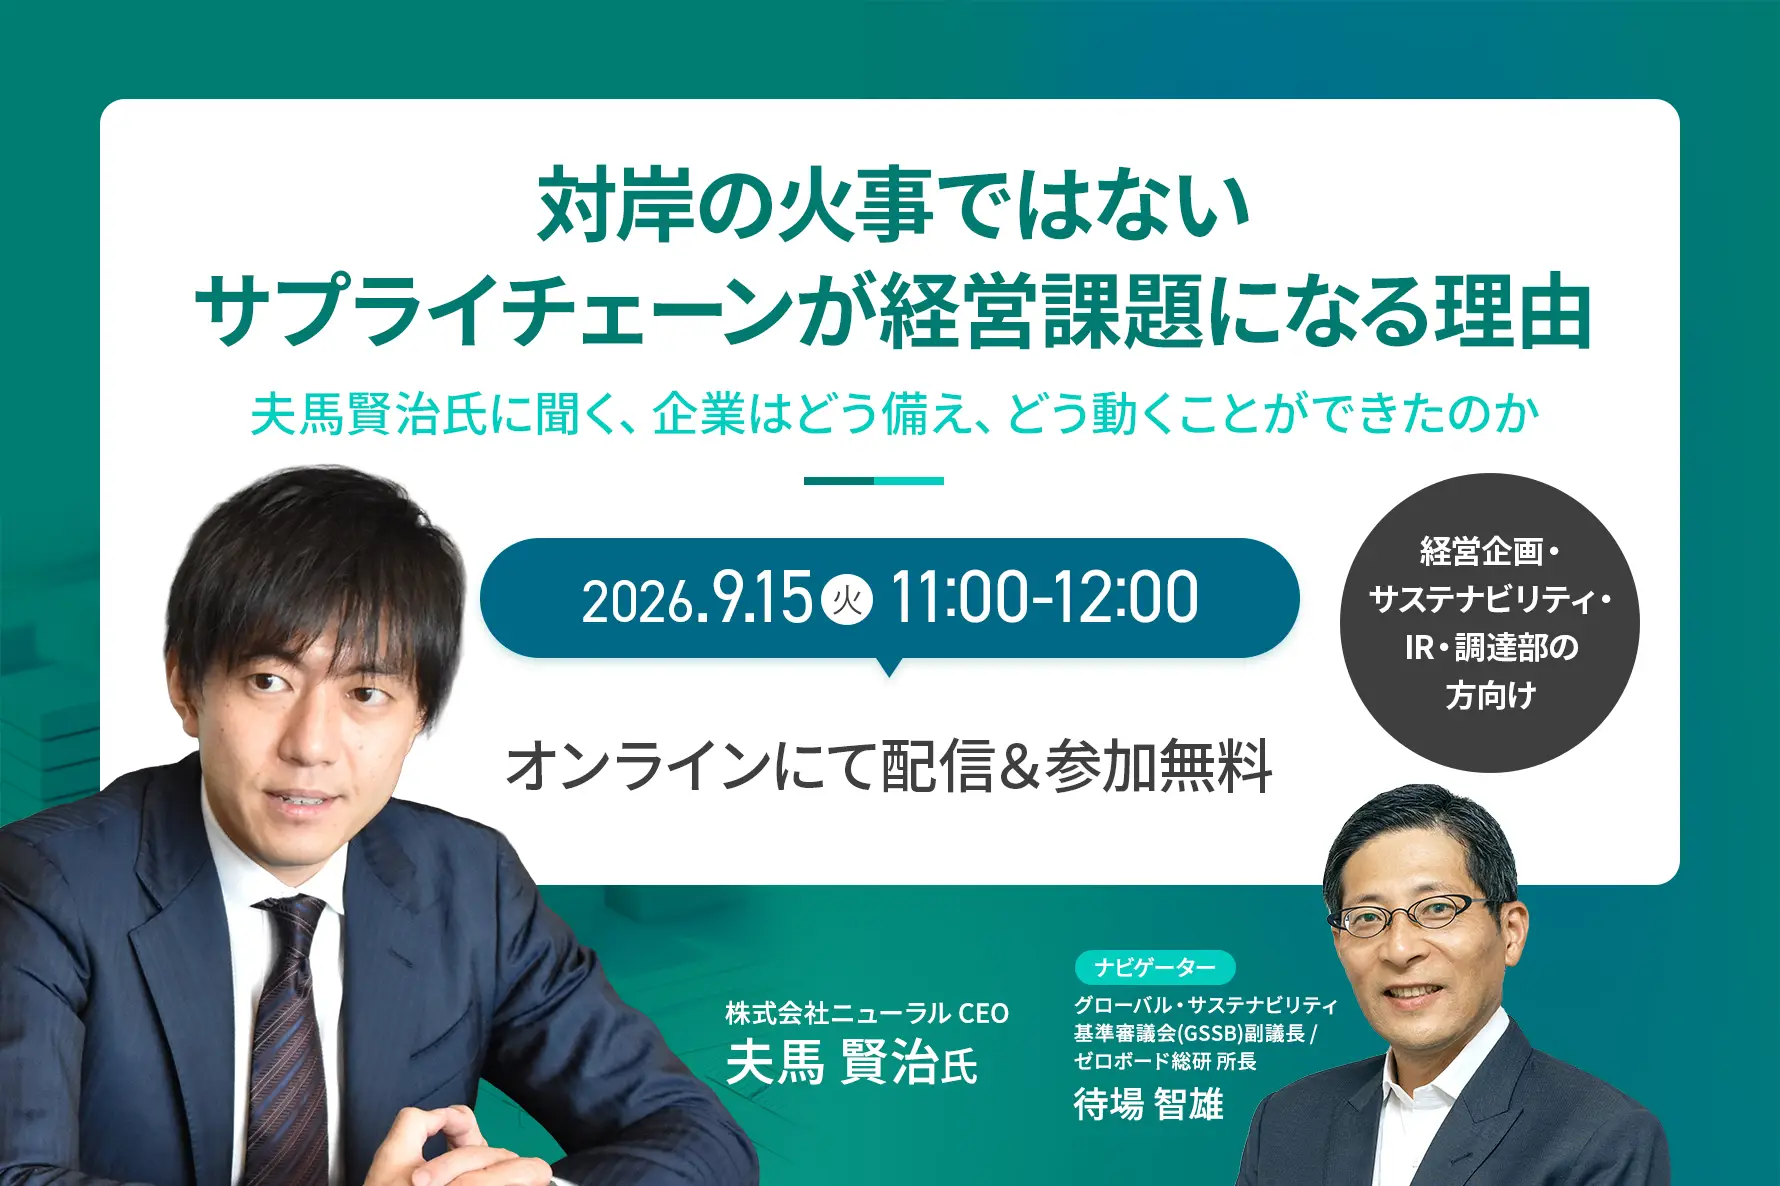
This is not someone else's problem—Why supply chains are becoming a management Issue: An interview with Kenji Fuma on how companies could have prepared and acted.
Location: Online (Zoom)Participation fee: Free -
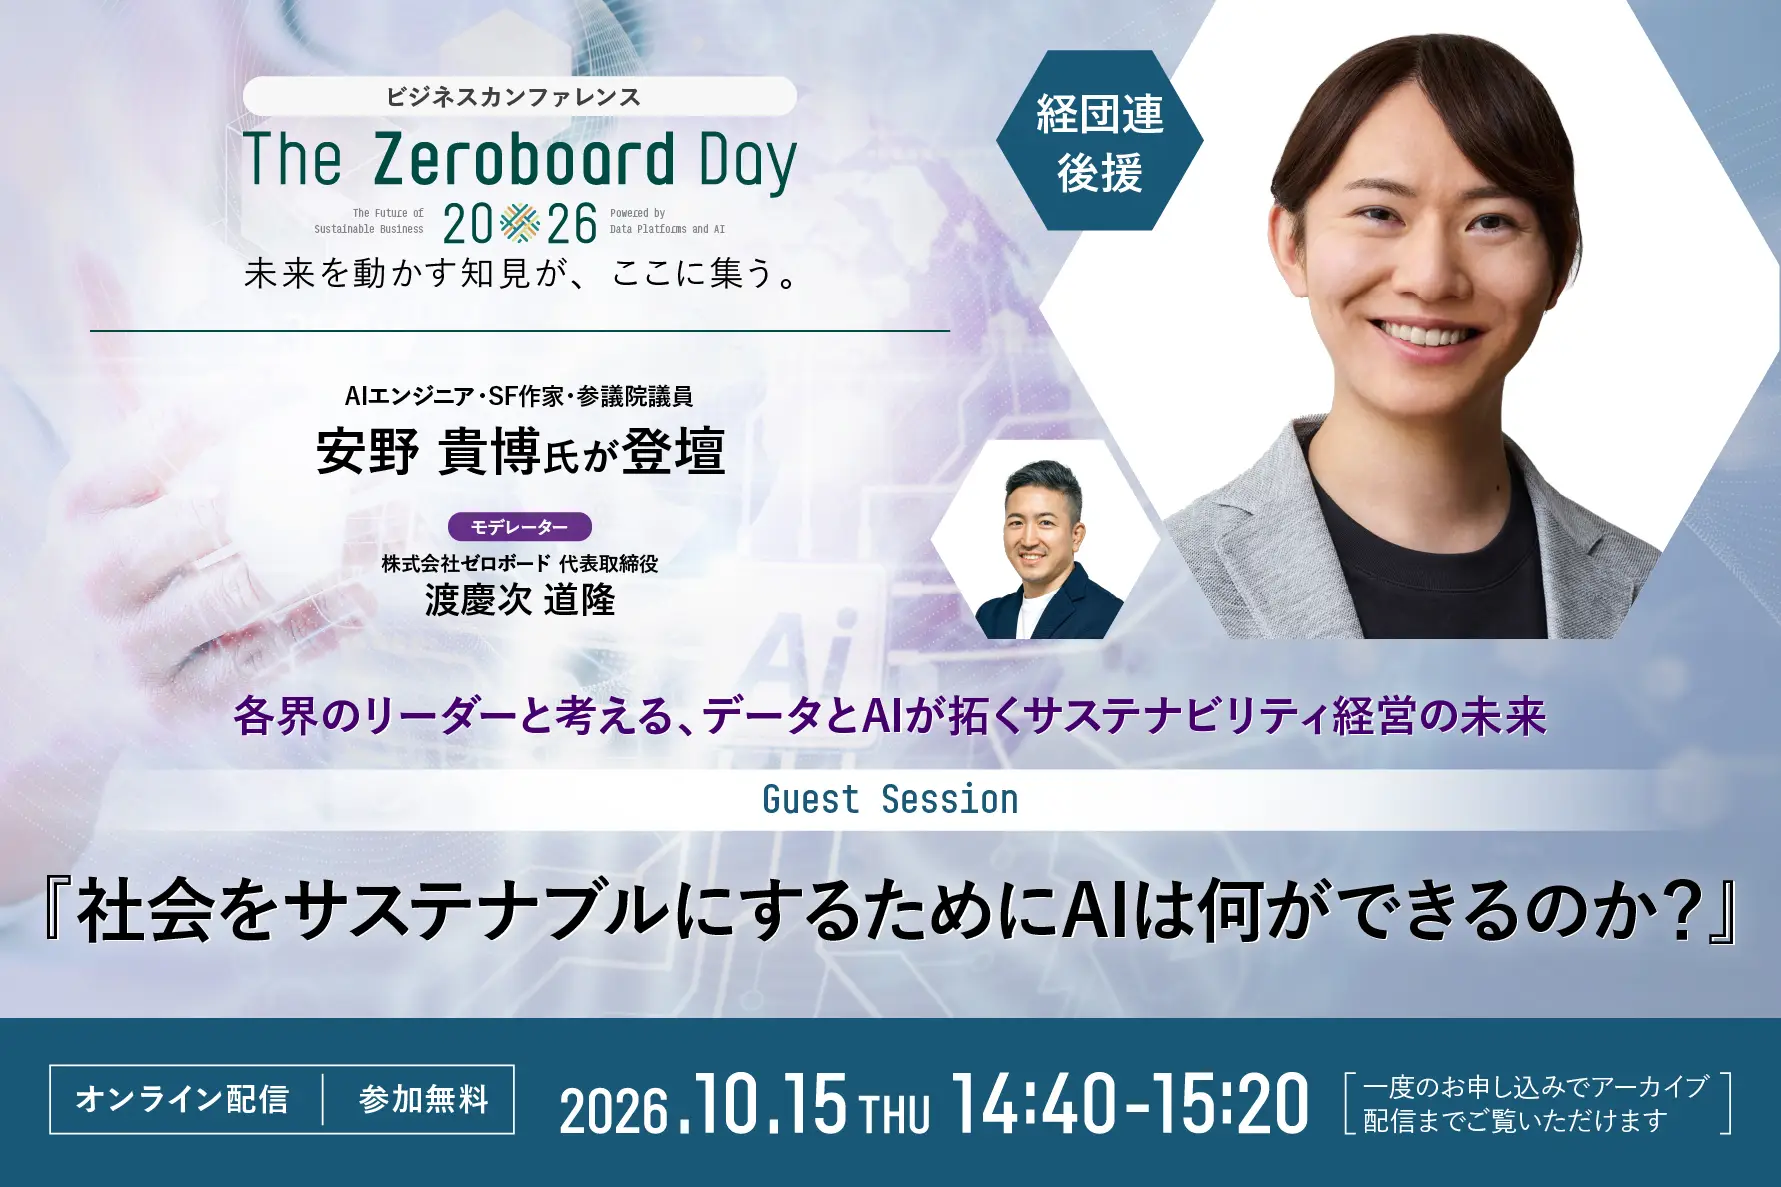
[Sponsored by Keidanren] What can AI do to make society sustainable?
~ Zeroboard's 5th Anniversary Conference "The Zeroboard Day 2026"~Location: Online (Zoom) *Archive streaming will be available at a later date.Participation fee: Free -
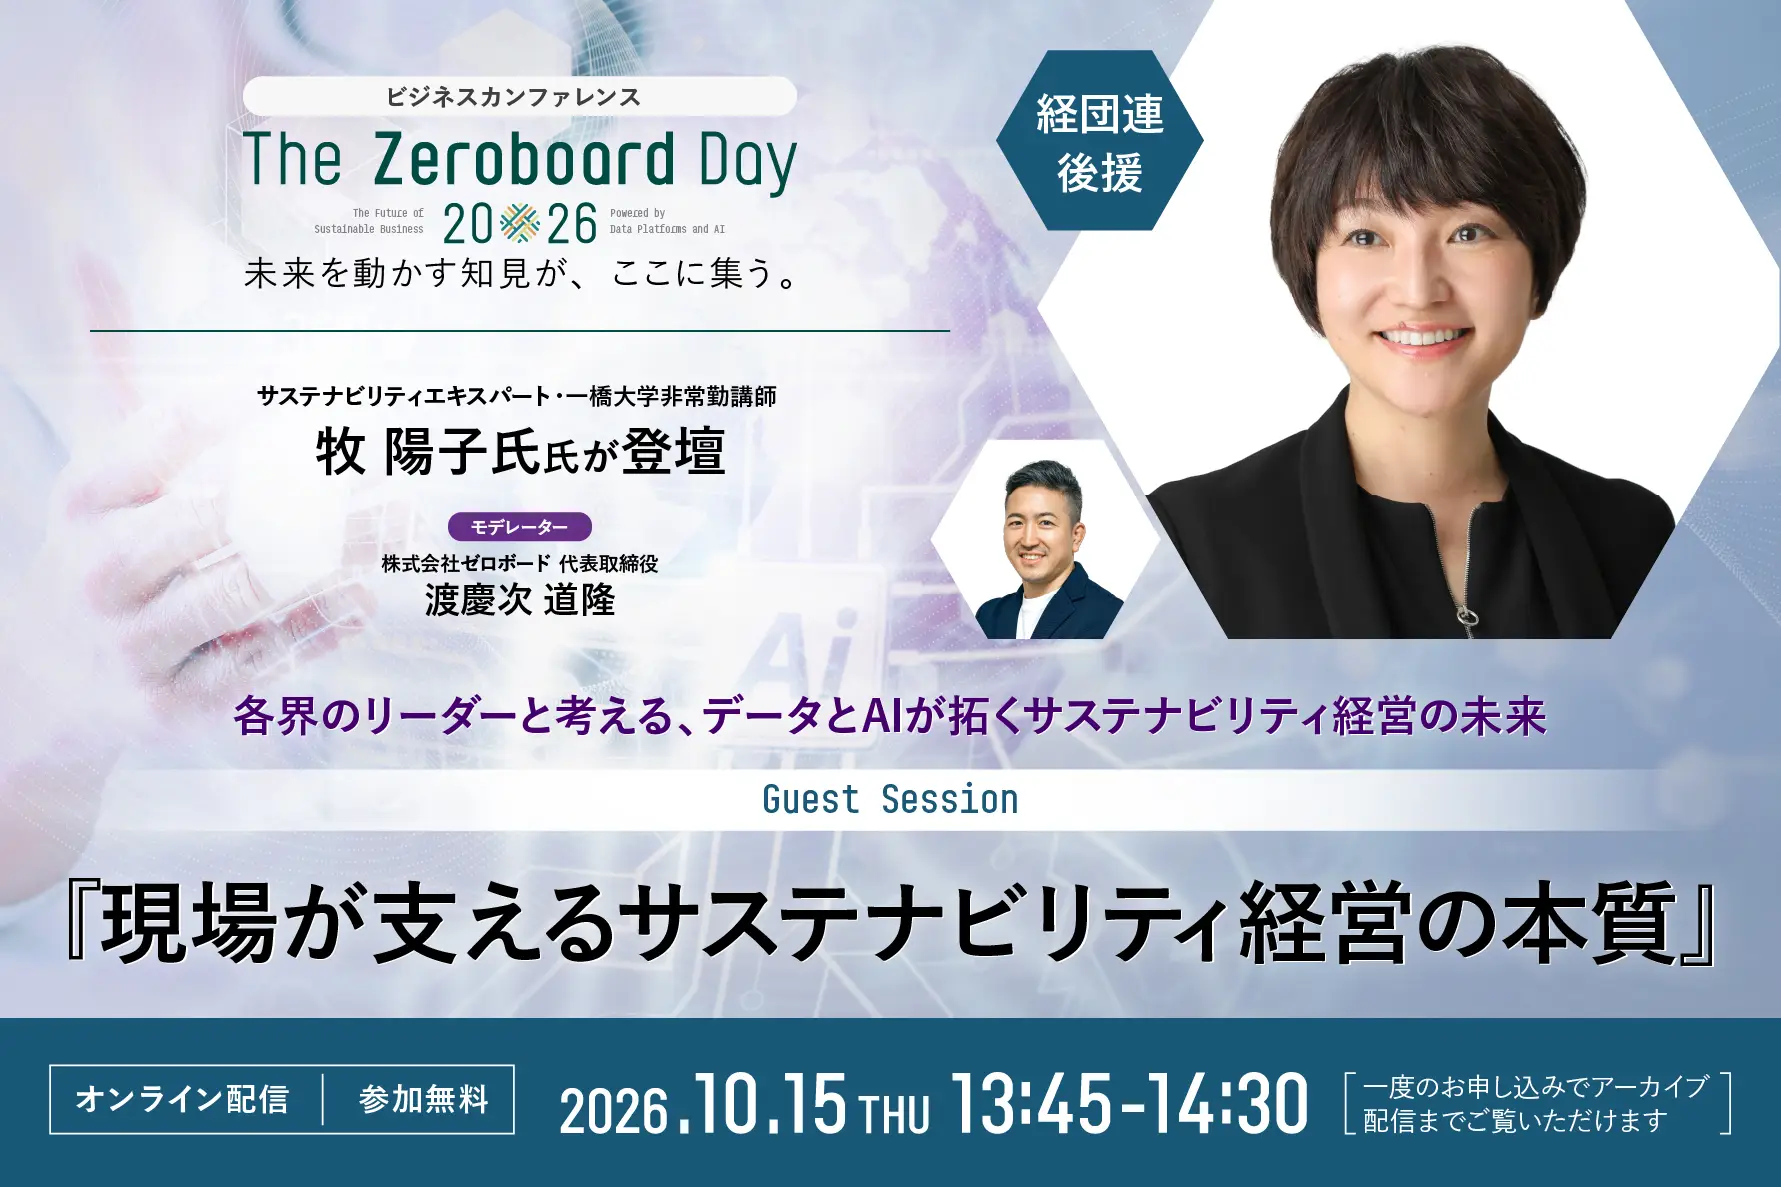
[Sponsored by Keidanren] The Essence of Sustainability Management Supported by the Front Lines: The Zeroboard 5th Anniversary Conference "The Zeroboard Day 2026"
Location: Online (Zoom) *Archive streaming will be available at a later date.Participation fee: Free
-
Deciphering the Exposure Draft of ESRS-40a, the Disclosure Standard for Non-EU Companies: Limitations on Impact and Value Chain Voluntary Standards (Public Comment Period Ends October 31)
-
Public comments on the revised GHG protocol Scope 2 have been released — Multiple methods to be considered due to disagreements over hourly matching, etc.
-
Measurement and Disclosure for Nature Positive "Implementation"—The Kumamoto Summit Revealed the Two Pillars of Impact and "Dependence"
-
What is Supply Chain Security? An explanation of implementation design and SCS evaluation systems to prevent procurement disruption risks.
-
Feeling the limitations of managing supplier surveys (CSR surveys) with Excel? How SAQ systemization can solve these problems.